

Ledger has confirmed an unauthorized hardware implant inside one customer’s wallet as investigators examine crypto thefts linked to devices purchased through Southeast Asian reseller CryptoBilis.
The losses are estimated at around $93.2 million, according to Bitquery, a blockchain analytics firm.
The hardware wallet manufacturers disclosed the finding on October 10, following reports of drained wallets a day earlier.
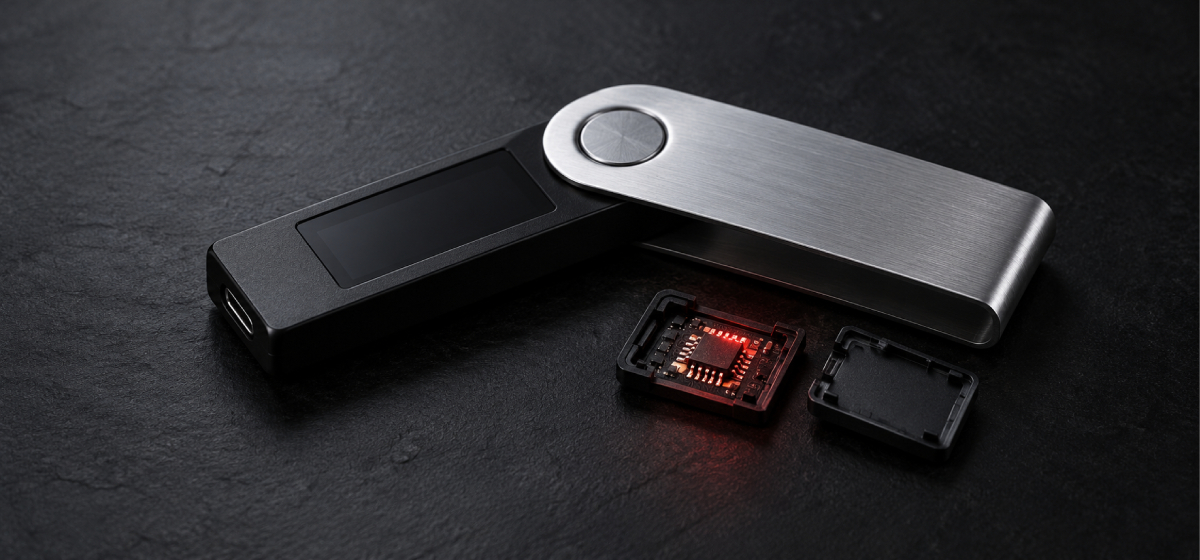
“Ledger can confirm that one of the impacted users’ devices contained an unauthorized hardware implant. Ledger is reaching out to impacted users as part of the ongoing investigation,” said Ledger.
CryptoBilis was listed as an unauthorized Ledger reseller serving Indonesia, Malaysia, and the Philippines.
Important Read: Ledger Wallet Review - Features, Models, and Security Explained
Loss Estimates Above $90 Million
Bitquery updated October 11 that $93.2 million left 315 wallets across TRON, Bitcoin, Ethereum, Solana, BNB Chain, and Polygon. The investigation also found that Tether froze approximately $10 million in USDT linked to the incident.
However, the total losses or number of affected customers are not yet confirmed by Ledger. Whether every reported theft involved the same implant remains unresolved.
Separately, former Mt. GOX CEO Mark Karpelès described an implant hidden behind a Ledger device’s screen that could capture recovery phrases during setup and transmit them over a cellular connection.
But these findings remain distinct from Ledger’s confirmed investigation results.
“Ledger will never ask for your 24-word recovery phrase,” said Ledger.
Reseller Suspends Sales
CryptoBilis has suspended sales of its entire hardware wallet inventory pending the investigation.
“As a measure of precaution CryptoBilis confirmed it has ceased sales of all hardware wallet inventory until the investigation is concluded. Ledger is in active communication with CryptoBilis on next steps,” said Ledger.
The crypto hardware wallet provider said the incident appeared isolated to the seller and its market, adding that its infrastructure, systems, and services were not compromised.
“We have no indication that Ledger’s security infrastructure, systems or services have been compromised,” said Ledger.
The affected buyers are advised by Ledger against setting up unused devices. Customers who have already initialized them should consider transferring assets to a new Ledger device with a new recovery phrase.
Sign up on WEEX and roll for a chance to win a share of the $1,000,000 prize pool.